Imperia
Security
Vulnerabilities with their fix in one go, antivirus from one interface, passwords and BitLocker keys kept safe.
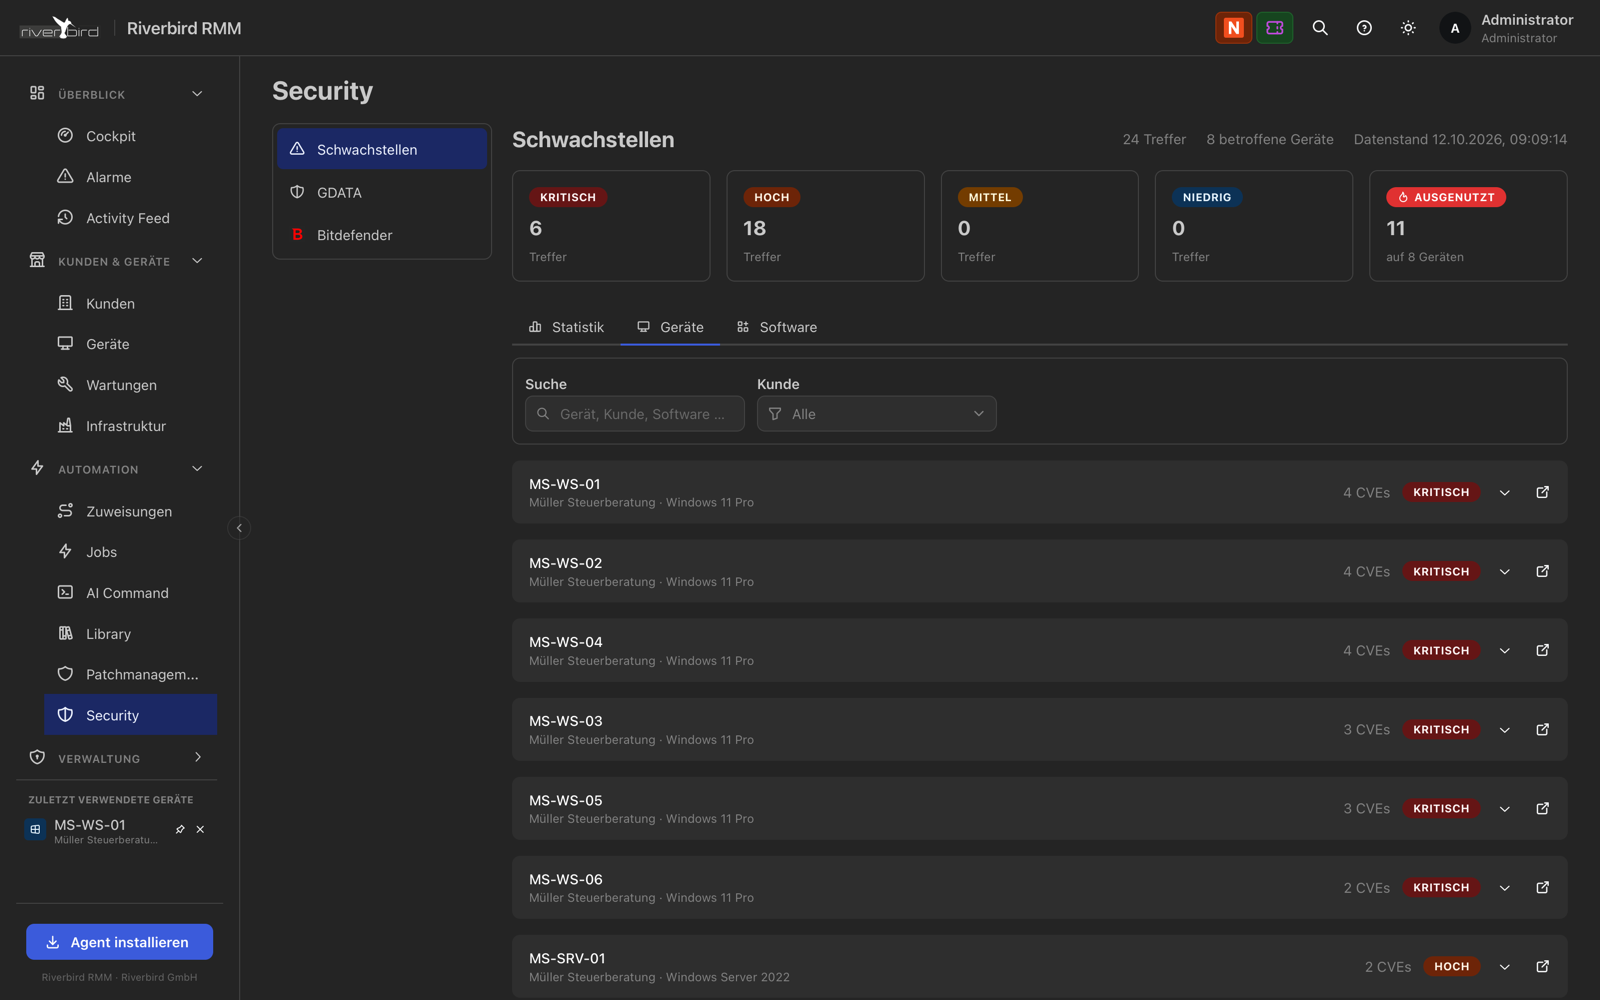
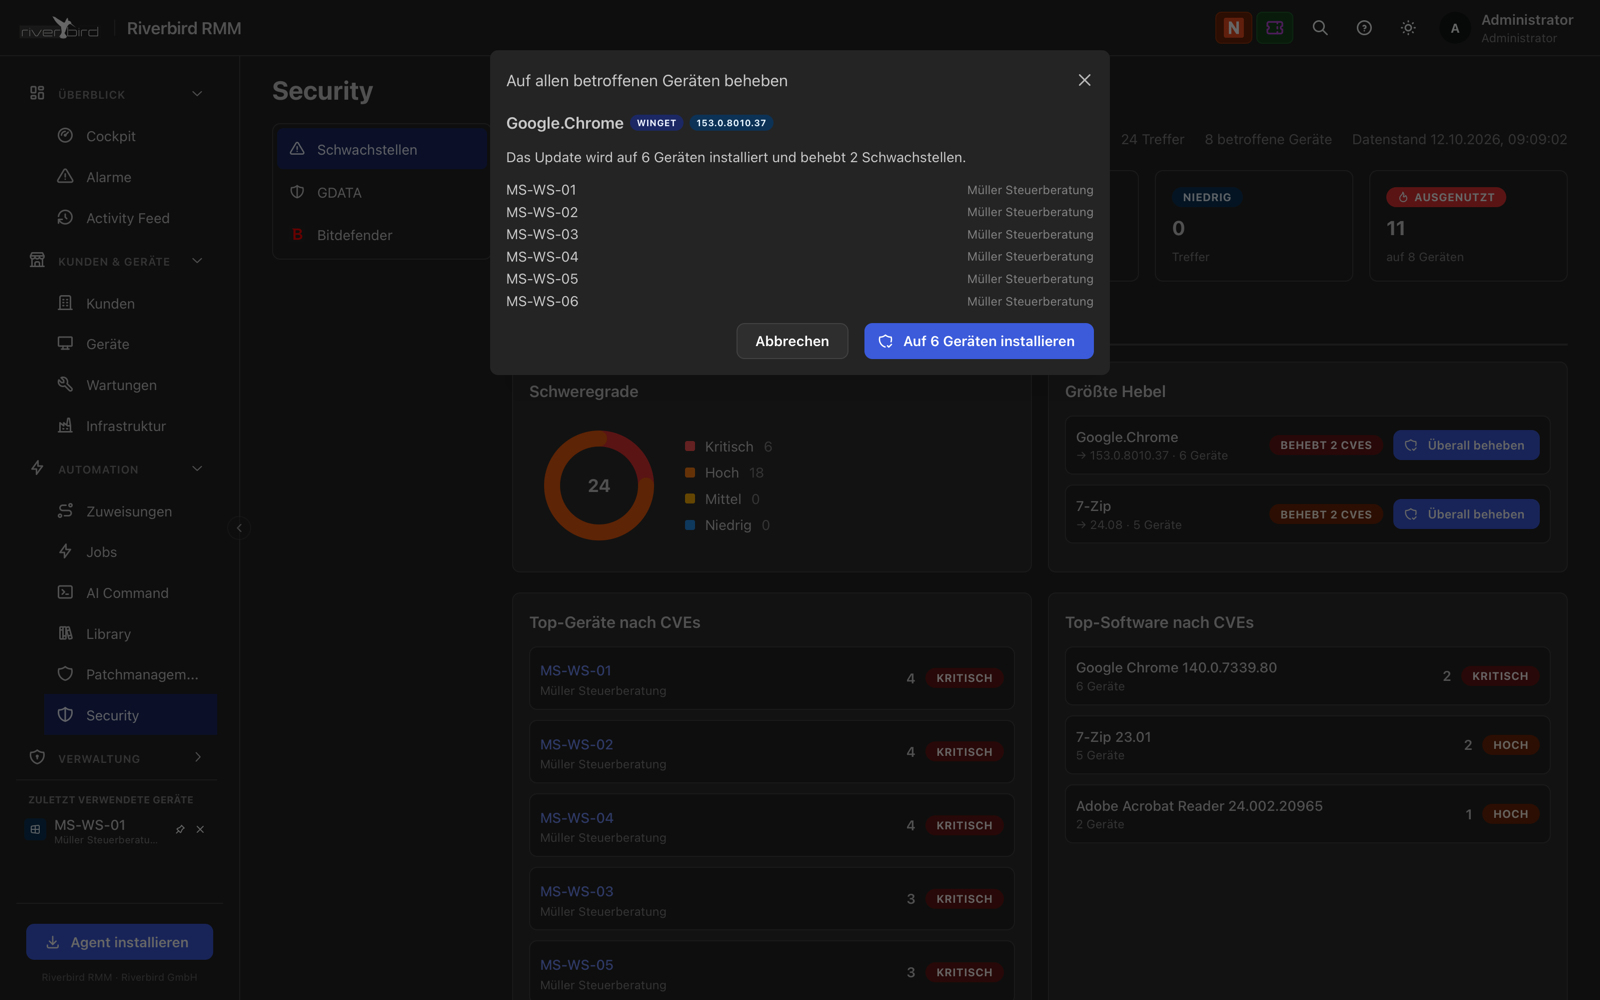
Imperia compares the software installed across your estate against known vulnerabilities and shows not just the finding but the way out: which update closes it, and on how many devices.
The matching service runs on our own infrastructure under the Falcon Secure brand. Alongside it sits a self-hosted store of leaked passwords that is queried anonymously — no password and no complete hash leaves your house.
Antivirus connects directly: G DATA, Bitdefender GravityZone and Securepoint. You see status, quarantine and rollout in the same cockpit as everything else, instead of in three vendor consoles.
Security in Imperia
Biggest leverage first
The list is sorted by effect: the update that closes forty findings at once is at the top.
Fix everywhere
One dialog rolls the update out to every affected device and then shows you what is left.
Password manager
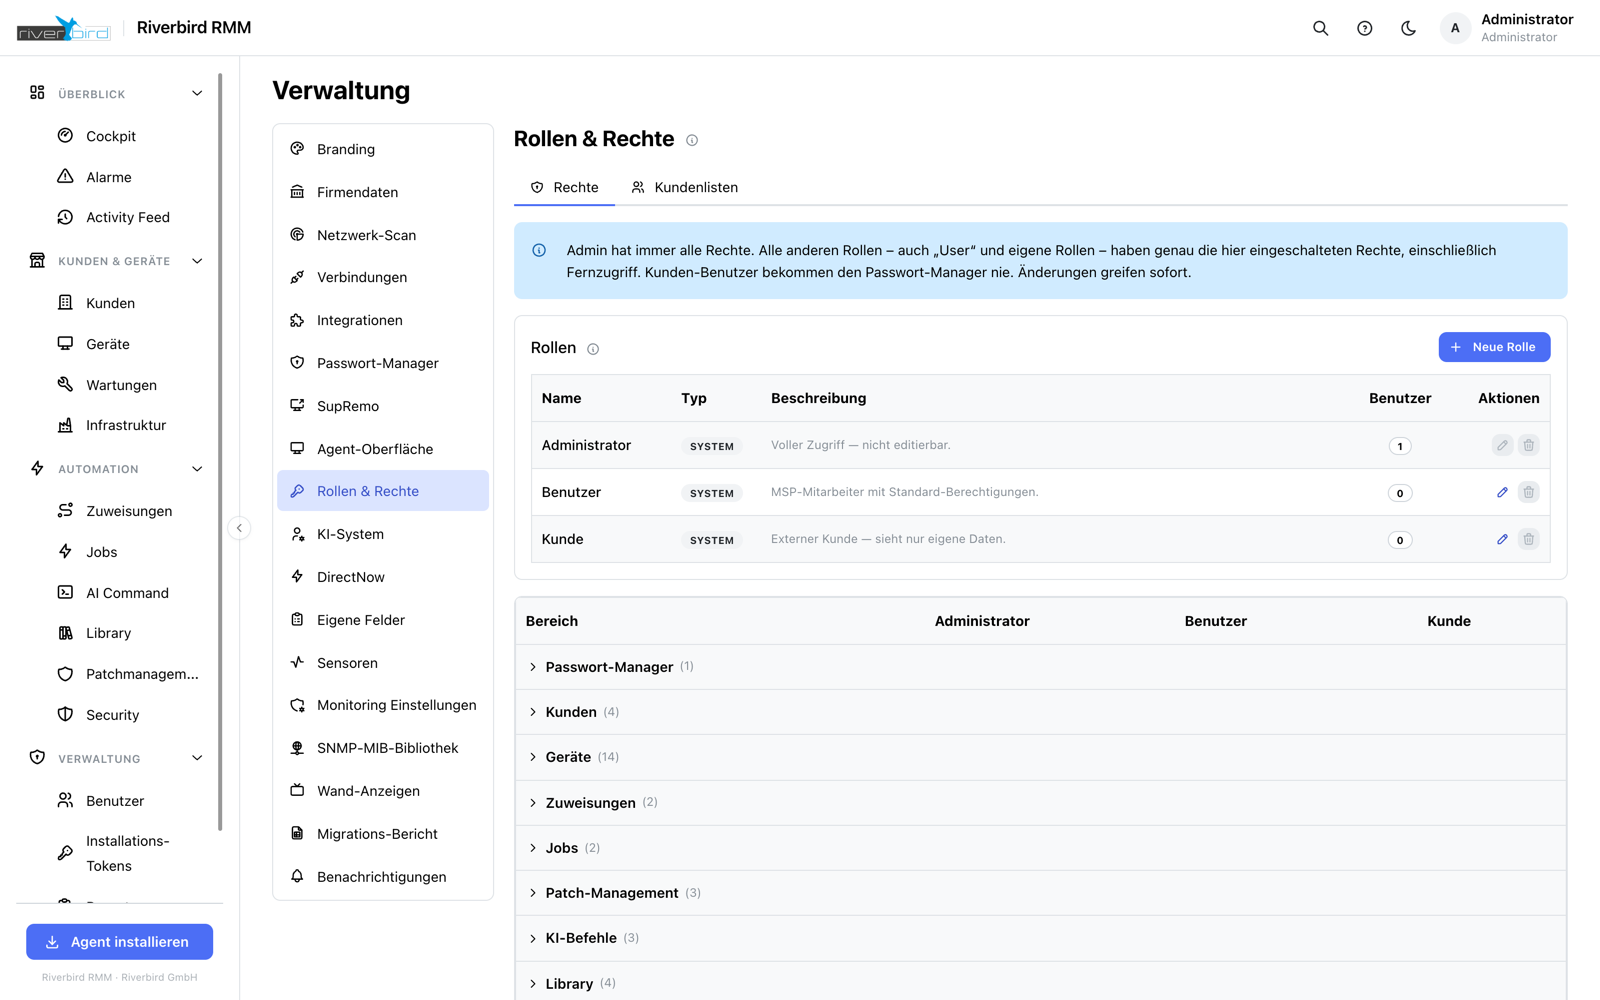
Passwords per customer, protected by permissions. Customer logins never get it.
BitLocker in one place
Recovery keys for every device in one place, visible only to those entitled to them.
Secure the way in
Two-factor sign-in, single sign-on with Microsoft Entra and invitations instead of e-mailed passwords.
Permissions to measure
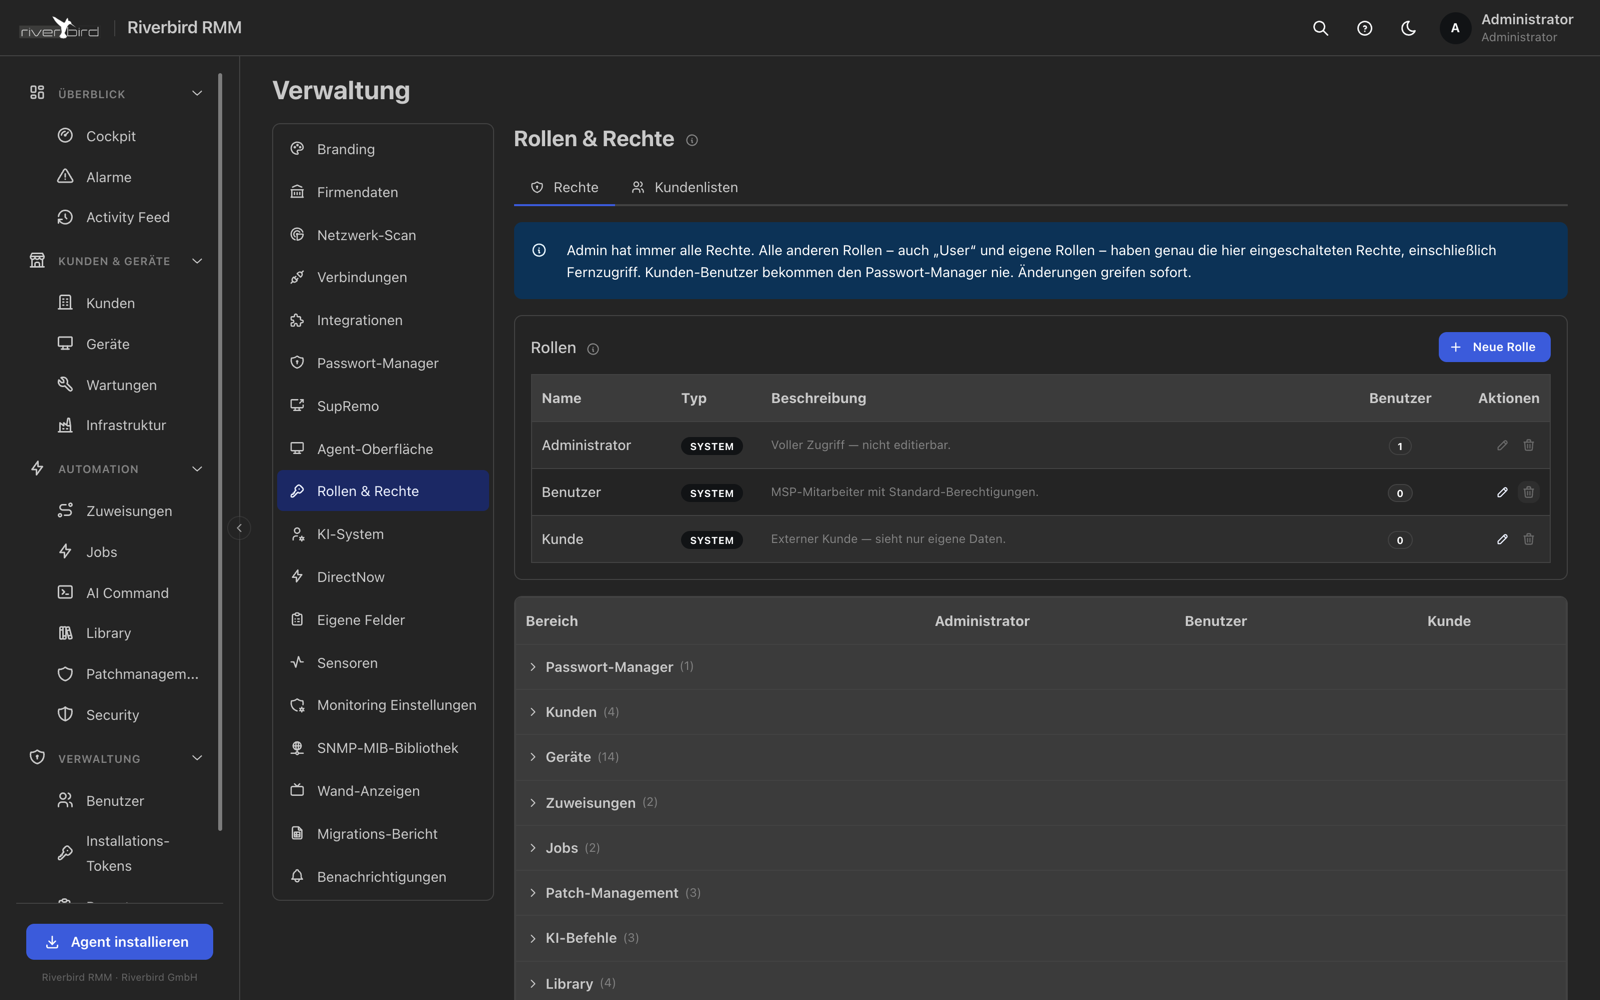
A freely configurable permission matrix instead of three fixed roles, with its own customer scope per role.
Falcon Secure
The vulnerability service is ours.
Behind the vulnerability view in Imperia sits Falcon Secure — our own matching service, run on our infrastructure in Germany. There is no third party that learns which software is running at which of your customers.
- Matching by CPE identifiers: Imperia reports which software is installed in which version and gets the relevant findings back — no host names, no customer names.
- Leaked passwords are checked against a store we host ourselves. The query is anonymised: neither a password nor a complete hash leaves your house.
- Exploited flaws are marked separately. What is demonstrably under attack comes before the rest.
- No second console. The finding, the devices affected and the fix sit in the same cockpit as monitoring and patches.
Common questions about Falcon Secure
Which data leaves our instance?
For the matching, the names and versions of the installed software as a CPE identifier. No host names, no customer names, no serial numbers.
How does the password check work?
Anonymously: Imperia sends only part of the hash and gets back a list of possible matches, which it evaluates itself. The service does not learn which password was meant.
Where does the vulnerability data come from?
From the public vulnerability catalogues, prepared on our side and kept up to date.
How is this different from a vulnerability scanner?
We do not scan the network; we evaluate what the agent inventories anyway. That costs no extra load on the devices and also finds software that is not visible from outside at all.
Is Falcon Secure part of Imperia or a separate product?
The matching is built into Imperia. Sales will advise you on the scope of your licence.
See Imperia in your own environment
We will set up a trial instance for you and walk through together what Imperia can do for your customers.